Skip to content

appsecwriteups.com

Learning AppSec Through Android & Web Vulnerability Writeups

  • Home
  • 🧑‍💻 Courses
  • Android
  • Web
  • Desktop
  • x86_64
  • Shielded
  • Home
  • 🧑‍💻 Courses
  • Android
  • Web
  • Desktop
  • x86_64
  • Shielded
Top Writeup
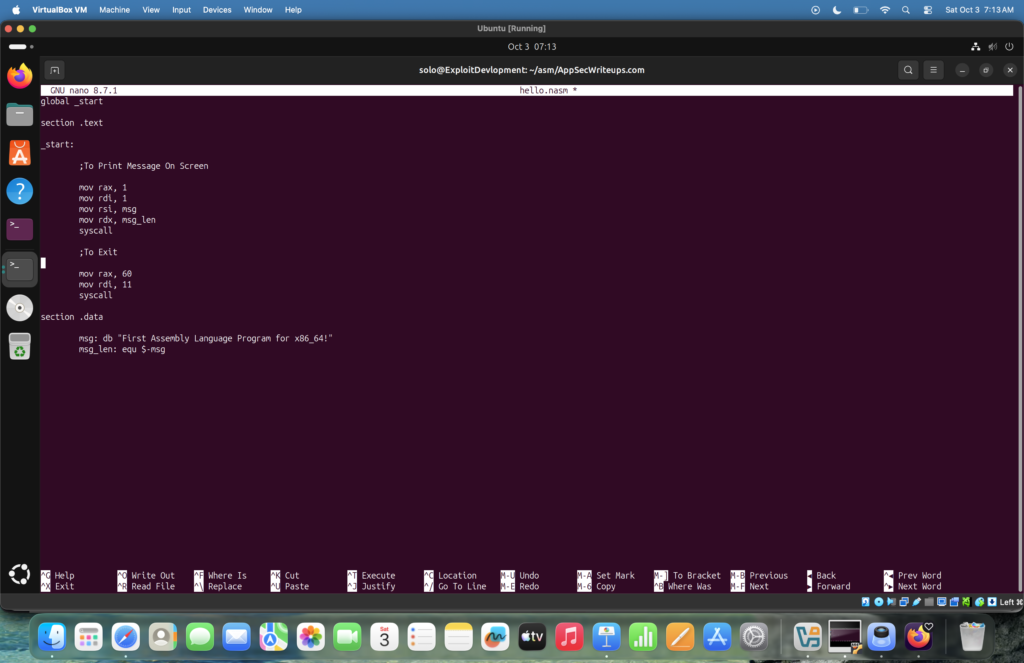
ASM[02] — [x86-64] Assembly Language: Understanding Registers and Writing Our First Program
Posted inx86_64

ASM[02] — [x86-64] Assembly Language: Understanding Registers and Writing Our First Program

Posted by By Jivan Magare October 3, 2026
Hello, I am Jivan, and in this writeup, you will learn about x86-64 Assembly by…
Read More
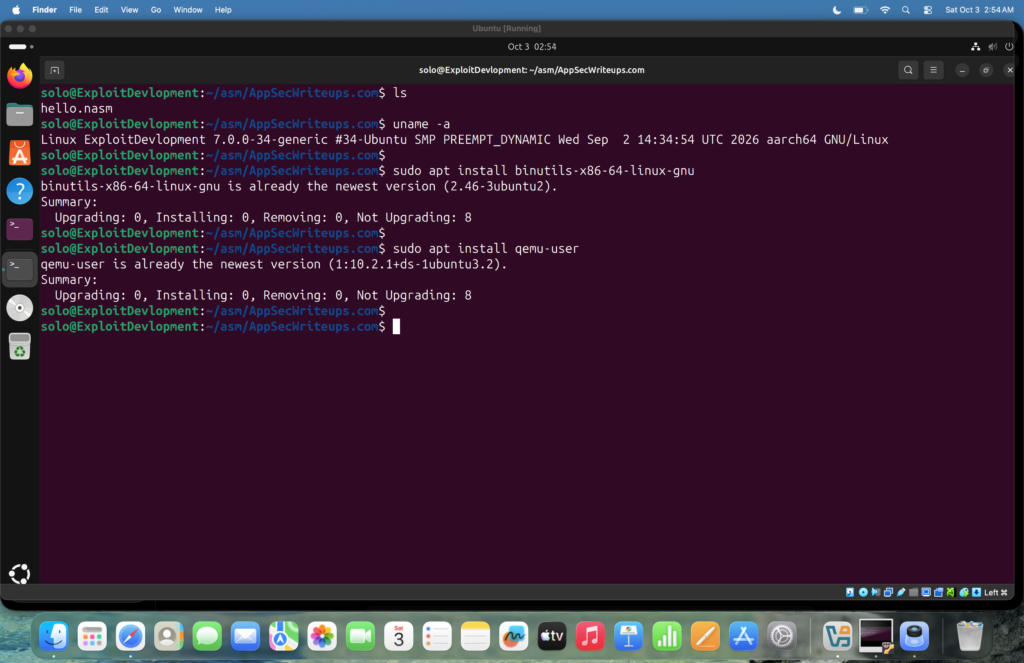
ASM[01] — [x86-64] Assembly Language: Environment Setup
Posted inx86_64

ASM[01] — [x86-64] Assembly Language: Environment Setup

Posted by By Jivan Magare October 3, 2026
Hello everyone! This writeup is not about any of my bug bounty findings. This series…
Read More
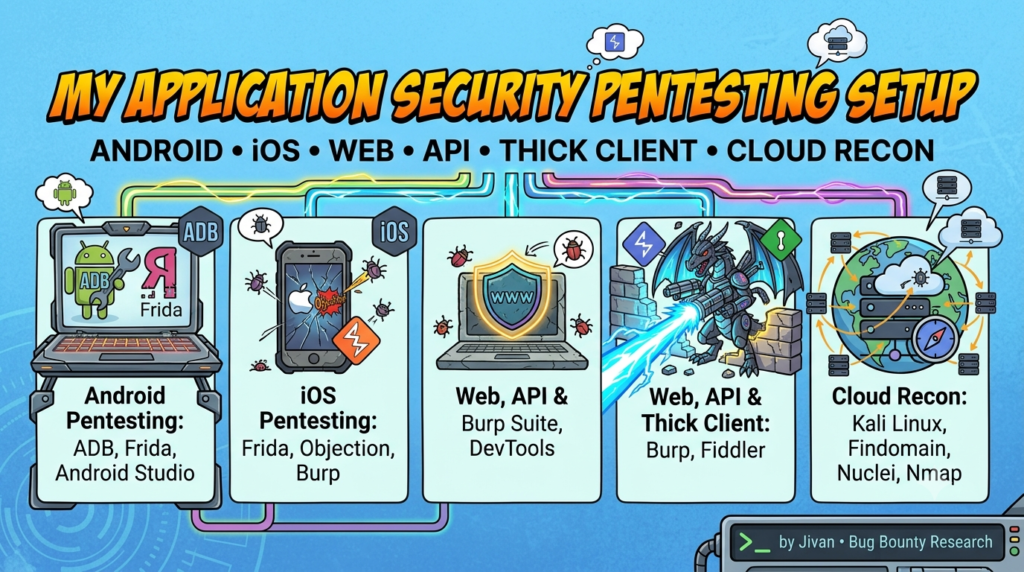
My Application Security Pentesting Setup: Android, iOS, Web, API, Thick Client & Cloud Recon
Posted inAndroid Desktop Web

My Application Security Pentesting Setup: Android, iOS, Web, API, Thick Client & Cloud Recon

Posted by By Jivan Magare September 29, 2026
Hello everyone! I’m Jivan, and in this post I want to share the application security…
Read More
Protected: How I Found Broken Access Control & How You Can Find It Too
Posted inWeb

Protected: How I Found Broken Access Control & How You Can Find It Too

Posted by By Jivan Magare September 4, 2026
Hello, and welcome back! I’m Jivan, and I’m back with another security write-up. In this…
Read More
Posted inWeb

Protected: Why a Critical-Looking Vulnerability Was Downgraded: Exposed SSH Credentials Explained

Posted by By Jivan Magare January 15, 2026
This content is password protected. To view it please go to the post page and enter the password.
Read More
Posted inDesktop

Protected: My First Day Pentesting Thick‑Client Apps — Discovered a Critical IDOR in a Desktop Client with a Full Black‑Box Approach

Posted by By Jivan Magare October 8, 2025
This content is password protected. To view it please go to the post page and enter the password.
Read More
How I Found a Critical Privilege Escalation That Let an Unprivileged User Become Admin and Earn $579 USD Bounty
Posted inWeb

How I Found a Critical Privilege Escalation That Let an Unprivileged User Become Admin and Earn $579 USD Bounty

Posted by By Jivan Magare October 7, 2025
Hi everyone — I’m back with a new writeup. I haven’t published for a few…
Read More
CSRF Account Deletion: How I Turned an “Excluded” Bug Into $87 USD Bounty
Posted inWeb

CSRF Account Deletion: How I Turned an “Excluded” Bug Into $87 USD Bounty

Posted by By Jivan Magare August 13, 2025
My name is Jivan, and in this case study, I will present a detailed analysis…
Read More
How to Identify and Handle Firebase Security Misconfigurations A Case Study
Posted inAndroid Web

How to Identify and Handle Firebase Security Misconfigurations A Case Study

Posted by By Jivan Magare July 31, 2025
Hello friends, I'm Jivan, and welcome to my latest write-up focused on Firebase misconfiguration from…
Read More
Security Testing via Black-Box Approach: Two Important Android App Issues Discovered Across the Same Company
Posted inAndroid

Security Testing via Black-Box Approach: Two Important Android App Issues Discovered Across the Same Company

Posted by By Jivan Magare June 25, 2025
Hello and welcome to AppSecWriteups.com! I’m Jivan Magare, and in today’s post, I’ll walk you…
Read More

Posts pagination

1 2 Next page

Archives

  • October 2026
  • September 2026
  • January 2026
  • October 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Comments

  1. Jivan Magare on Protected: My First Day Pentesting Thick‑Client Apps — Discovered a Critical IDOR in a Desktop Client with a Full Black‑Box Approach
  2. Shubham on Protected: My First Day Pentesting Thick‑Client Apps — Discovered a Critical IDOR in a Desktop Client with a Full Black‑Box Approach
  3. Jivan Magare on How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues
  4. Shubham on How I Found a No Rate Limit Vulnerability on a Login Endpoint, Earned a 100€ Bounty, and My Approach to Testing for No Rate Limit Issues
  5. Jivan Magare on CSRF Account Deletion: How I Turned an “Excluded” Bug Into $87 USD Bounty

Recent Posts

  • ASM[02] — [x86-64] Assembly Language: Understanding Registers and Writing Our First Program
  • ASM[01] — [x86-64] Assembly Language: Environment Setup
  • My Application Security Pentesting Setup: Android, iOS, Web, API, Thick Client & Cloud Recon
  • Protected: How I Found Broken Access Control & How You Can Find It Too
  • Protected: Why a Critical-Looking Vulnerability Was Downgraded: Exposed SSH Credentials Explained

Categories

  • Android
  • Desktop
  • Web
  • x86_64
Post You Might Like
Posted inx86_64
ASM[02] — [x86-64] Assembly Language: Understanding Registers and Writing Our First Program
Posted by By Jivan Magare October 3, 2026
Posted inx86_64
ASM[01] — [x86-64] Assembly Language: Environment Setup
Posted by By Jivan Magare October 3, 2026
Posted inAndroid Desktop Web
My Application Security Pentesting Setup: Android, iOS, Web, API, Thick Client & Cloud Recon
Posted by By Jivan Magare September 29, 2026
Posted inWeb
Protected: How I Found Broken Access Control & How You Can Find It Too
Posted by By Jivan Magare September 4, 2026

đź”—Follow Me

  • LinkedIn

đź’¬Contact Us

đź“© Have questions, suggestions, or found a security issue? Reach out to us at: contact@appsecwriteups.com

🛡️Privacy Policy

Privacy Policy

Copyright 2026 — appsecwriteups.com. All rights reserved. appsecwriteups.com
Scroll to Top